Map your agents
See every agent in your code, what it can reach, and which ones need care first. Then keep the map current with rescans and a CI check.
Open the agent map
Open Agents. Each agent is drawn with its user, its model, its tools and the documents it reads. Click any node or line for its details on the right.
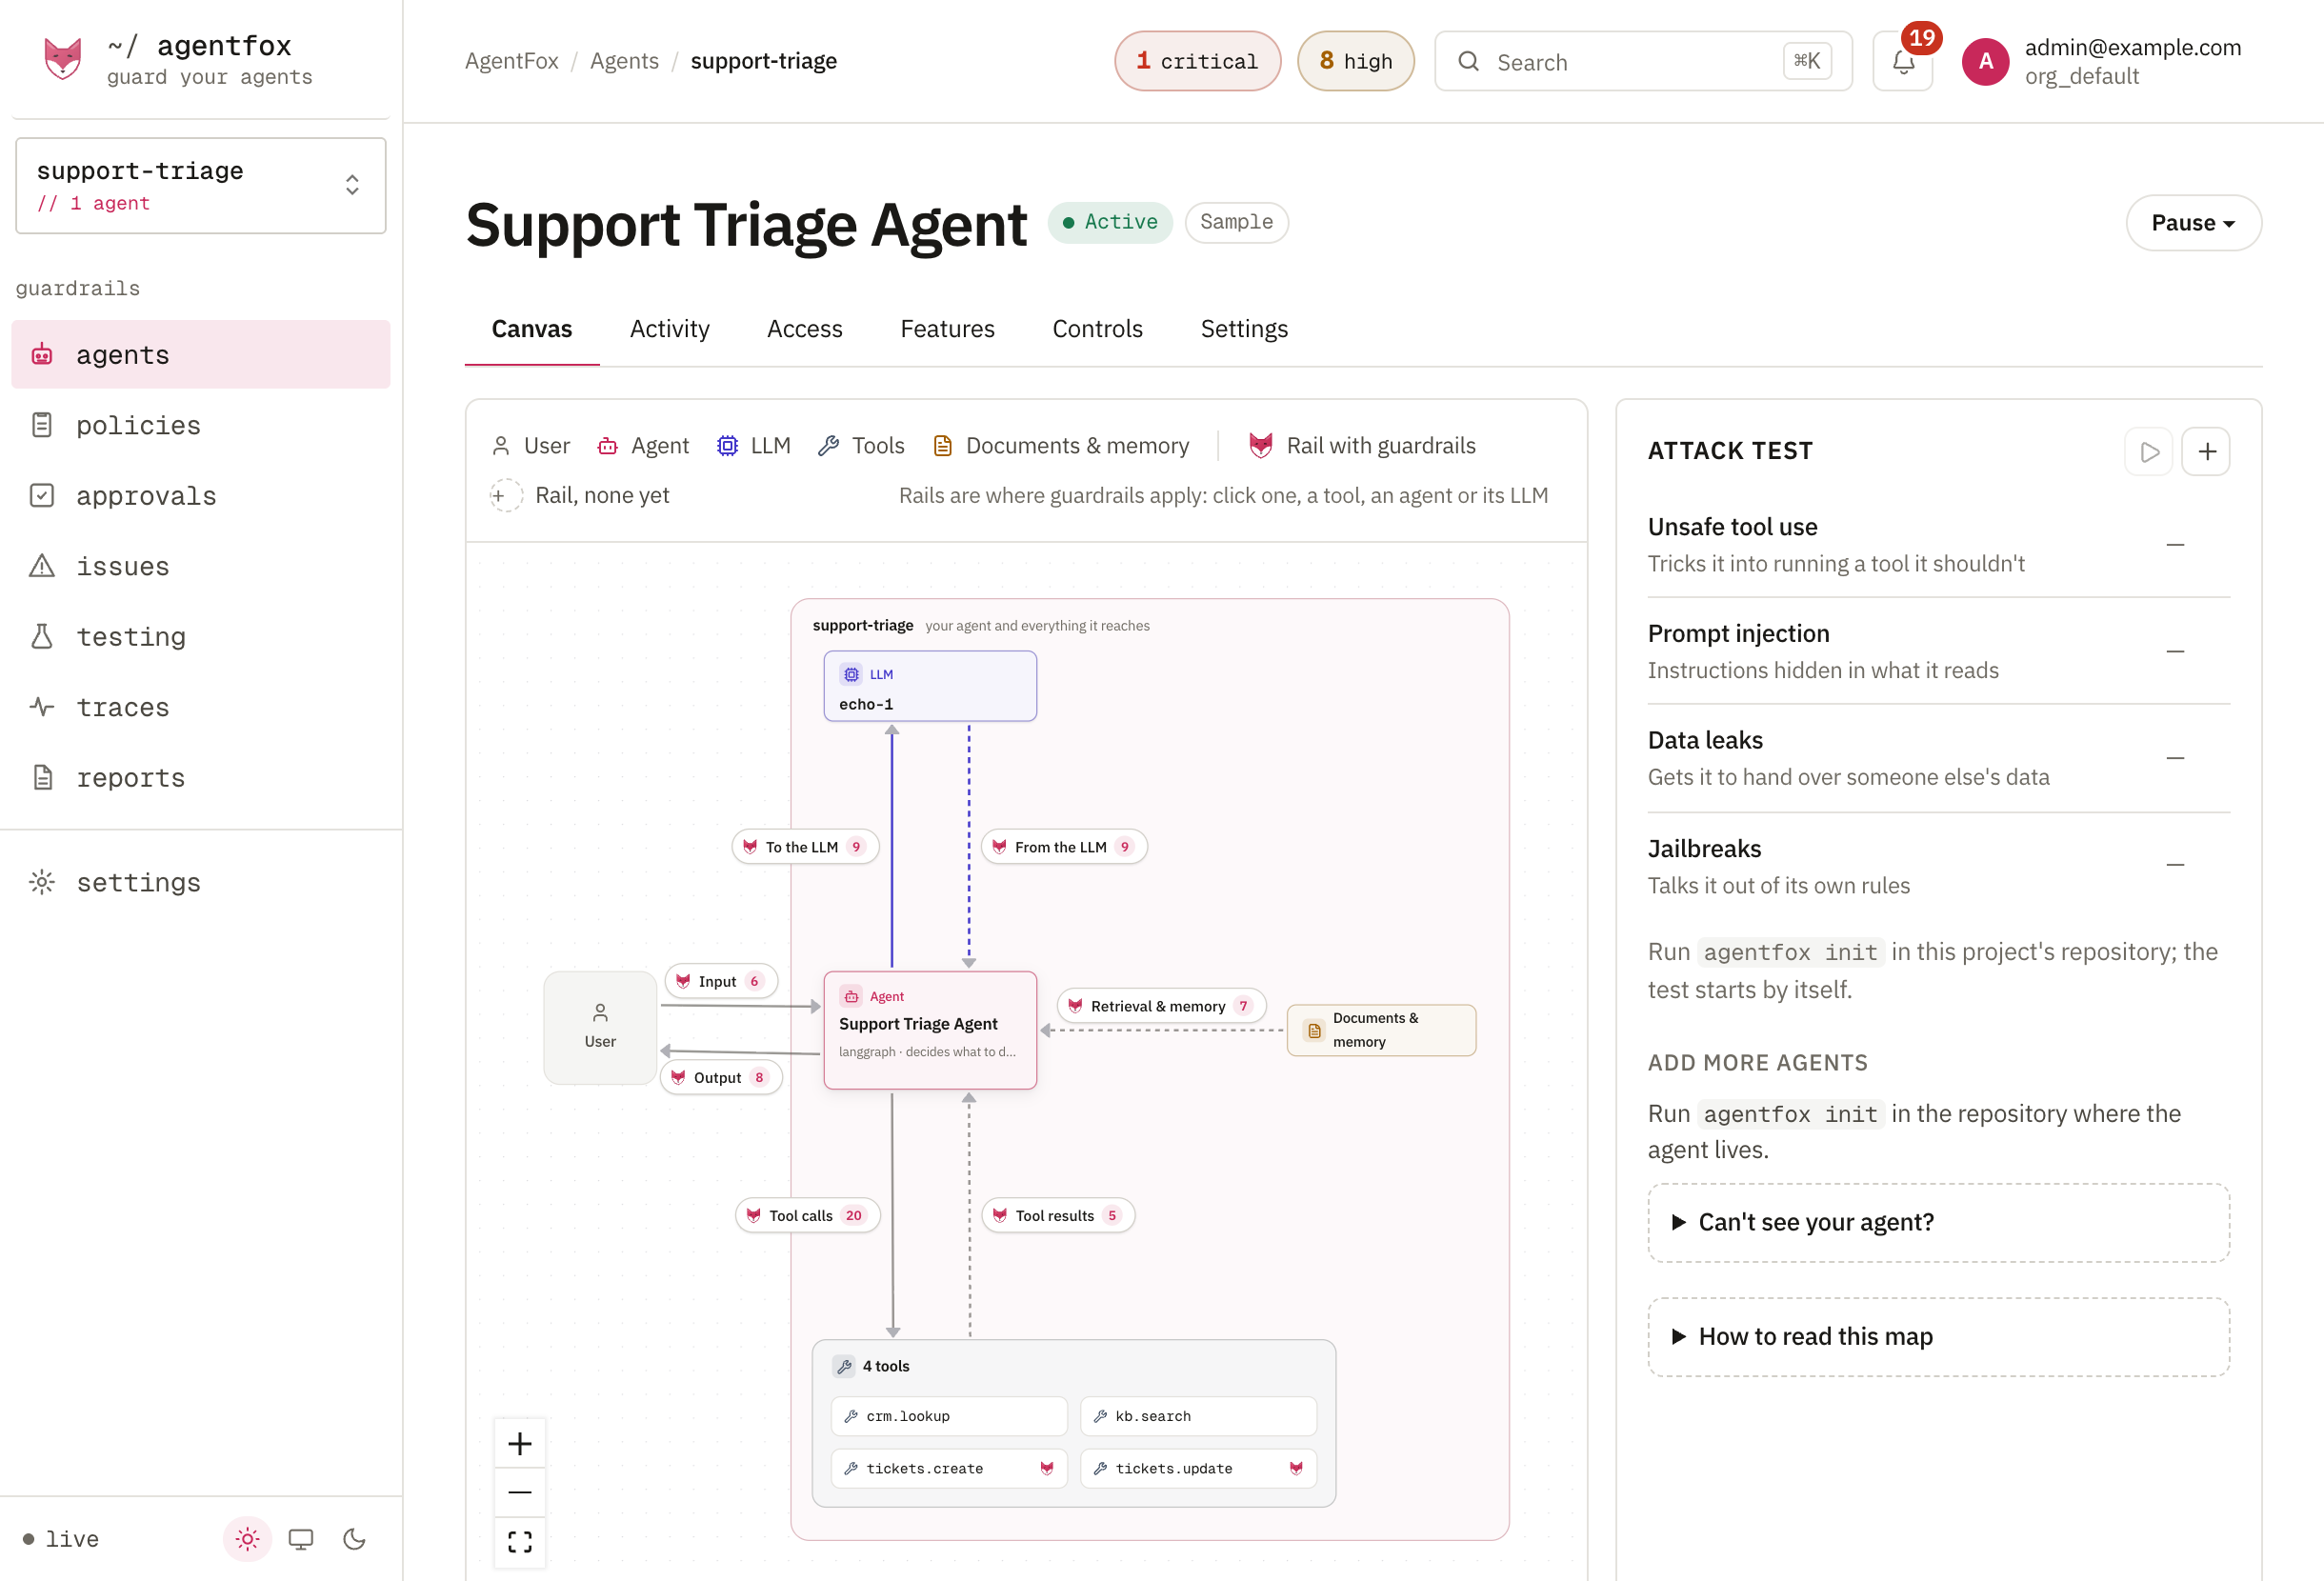
Read the lines and labels
A line is a place where a guardrail can run: the user's message, the reply, a tool call, a tool's result. A line with our mark has guardrails on it; a + means none yet. Each tool carries its impact: Read only, Writes, High impact or Irreversible.
Connect a GitHub repository
In Settings → Connections, press Connect GitHub, then Scan next to a repository. The code is read, never run. New agents arrive on Agents as drafts until you add them.
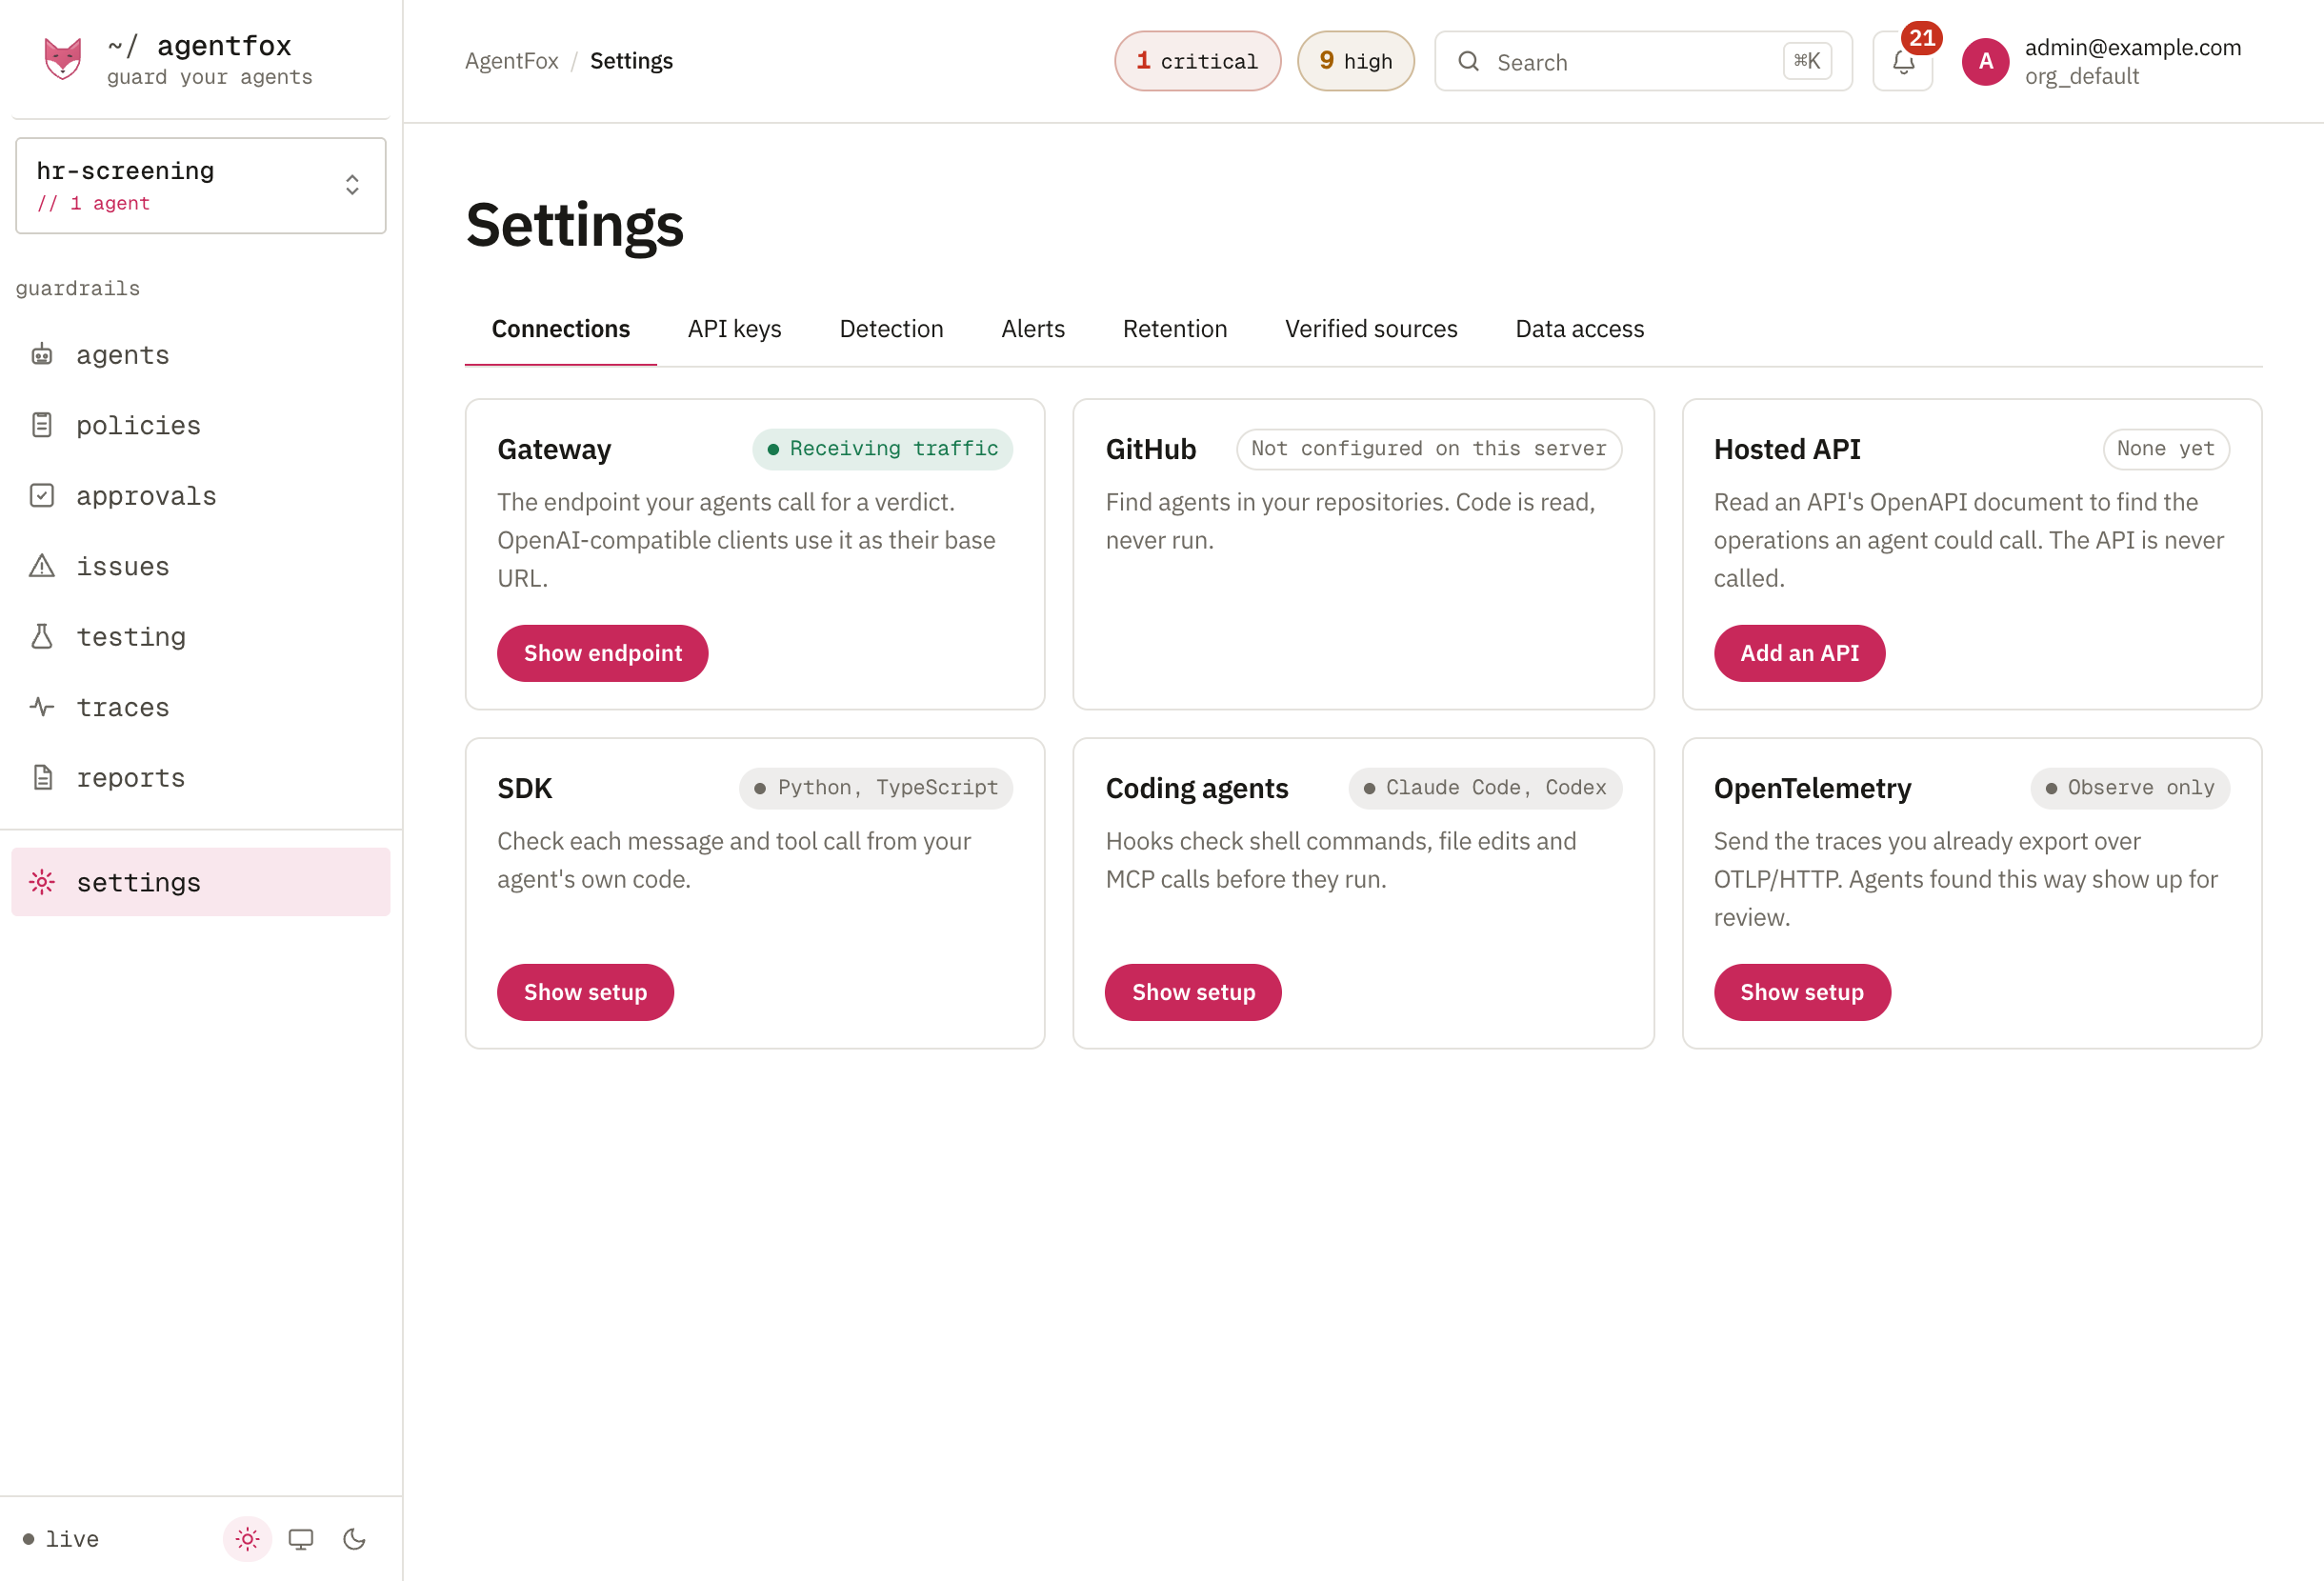
A scanned repository is rescanned every six hours. A new tool, a model call that lost its guardrails, or a new risky combination of tools becomes an Issue.
Scan in CI
Run the scan in any CI job.
--failfails the job when a model call has no guardrails. Nothing is sent anywhere.bash pip install agentfox agentfox scan --fail --no-submit
The pattern to fix first
An agent is at risk when it holds all three of these at once: a tool that reads private data, a tool that reads content an outsider can write (a web page, an email, an issue comment), and a tool that can send data out. An instruction hidden in that content can then make it send your data somewhere. The scan names the three tools and the fix. Usually the fix is to require approval on the tool that sends out (see Tool access).
What the scan reads
- Python, TypeScript and JavaScript. Agents in the OpenAI and Anthropic SDKs, LangGraph, LangChain, CrewAI, AutoGen and Google ADK, and who hands work to whom.
- MCP servers from
.mcp.json, Cursor, Claude Code and Claude Desktop configs. - Not tools built at runtime, for example loaded from a database. Agents that send traffic show up anyway, marked unregistered.
If something goes wrong
| You see | Do this |
|---|---|
| The scan proposes nothing | The agent sits behind a wrapper the scan does not know. Connect it with one line in Python instead. |
| A tool has the wrong impact | Change it on the agent's Access page. Your choice always wins over the guess. |
| Connecting GitHub fails with 503 | A self-hosted gateway needs AGENTFOX_TOKEN_ENCRYPTION_KEY to store the GitHub token. |